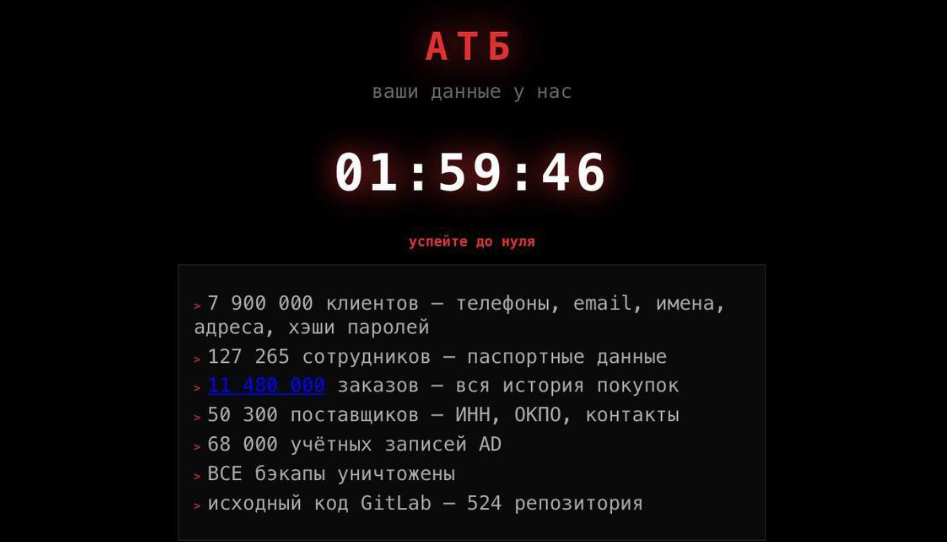
A report has circulated online alleging a large-scale cyberattack on ATB’s information systems. Unidentified individuals claim to have gained access to the data of millions of the company’s customers, staff and suppliers, and are demanding $400 thousand in cryptocurrency, threatening to make the stolen information public. At the time of publication, there is no independent confirmation of the alleged scale of the leak.
What the perpetrators are claiming
The screenshot that has been published shows a page featuring a timer and a list of information to which the unknown individuals allegedly gained access. They claim that the stolen data may include details of approximately 7.9 million customers, including telephone numbers, email addresses, names, addresses and password hashes.
The authors of the report also claim to have access to data on more than 127,000 employees, stories roughly 11.48 million orders, information on tens of thousands of suppliers, corporate infrastructure accounts and software code repositories.
They are demanding $400 thousand for the data
The authors of the notice demanded that the company pay $400 thousand in cryptocurrency. The page specifies a time limit for transferring the funds, after which the stolen information is allegedly set to be made publicly available.
This type of scheme is typical of cybercriminal groups that use data theft as a means of blackmail: they give companies a limited time to pay, threatening to publish the databases or sell them.
The mere fact that such a report has appeared, however, does not in itself prove that all the data cited was actually obtained.
There has been no official statement from ATB as yet
At the time of writing, on the official corporate news page ATB No separate statement has been issued regarding a large-scale data breach or a ransom demand. The company’s most recent available reports relate to its operational activities.
If the company confirms the incident, the key questions will be the actual volume of data compromised, the duration of the unauthorised access, and whether passwords or other information enabling access to users’ accounts were obtained.
What ATB customers should do
There is no need to panic until the official results of the investigation are released, but users of ATB’s services are advised to follow basic digital security guidelines. If the password for your ATB account has also been used on other websites, it is best to change it there first. You should pay particular attention to emails, text messages and messages on messaging apps, which may be disguised as communications from ATB.
Following major data breaches, fraudsters often use the contact details they have obtained for phishing — for example, by sending messages about «refunds», «account verification» or «compensation». You should not click on suspicious links or enter your bank details on third-party websites.